GDPR checklist for small businesses
Cookies and visitor information: two points to check on the site of a small business or SME, without confusing them with a full compliance audit.
The GDPR also applies to small businesses processing personal data. Cookies and visitor information are the first two website checks. They do not establish compliance across the whole business.
1. Cookies and visitors' choices
Trackers requiring consent, including advertising trackers, must stay blocked until the visitor accepts. Some trackers are exempt, including those strictly necessary for the requested service and certain audience measurement tools under specific conditions. Check each tool's actual use and configuration: its name alone does not establish an exemption.
Accepting and refusing must be equally easy. Continuing to browse does not count as consent, and consent must be easy to withdraw. The CNIL details the rules applicable to cookies and tracers.
2. Personal data information
When a form collects data, the visitor must be informed at the time of collection. A first mention can refer to a privacy policy that is accessible and adapted to the processing of the site.
This information should identify the controller, purposes and legal basis of processing, recipients, retention periods, rights and how to exercise them. Other details depend on the processing, such as transfers outside the European Union. The CNIL fact sheet on people's information helps to prepare these elements.
2Cafés can intervene on tool settings and integration of validated texts. Compliance also requires a review of company practices, contracts, security and data; the installation of a banner does not guarantee it.
Read next.
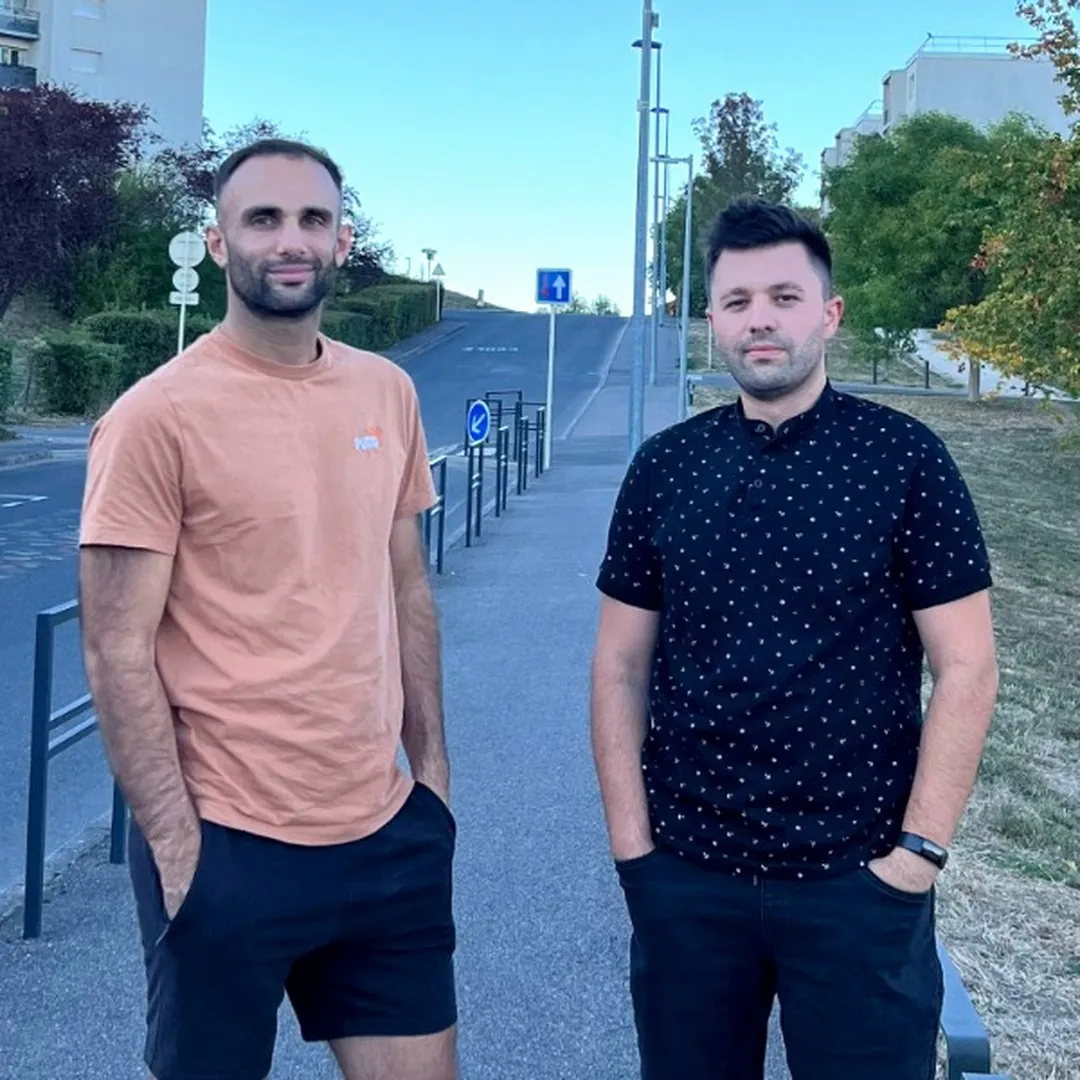
The beginnings of 2Cafés
Andrei Chirtes and Anthony Grasso met while studying Networks and Telecommunications. Here is how their shared ideas led to 2Cafés.
Read the article
Email campaign platform or custom-built tool?
Brevo, Mailchimp, a French platform or custom development: practical criteria for choosing without paying for unnecessary complexity or blocking your process.
Read the article
Case study: an email campaign to 33,100 contacts
How a custom email tool helped prepare, test and run a campaign to 33,100 contacts over 18 days, with precise acceptance and rejection tracking.
Read the article