LexCase Avocats
Designing a law firm website with several offices.
Read the case studyCase study · Security
Le Cordographe’s business website had been compromised. We rebuilt a clean WordPress foundation, brought the website back online and verified that discovery, demo and contact pages worked again.
The starting point
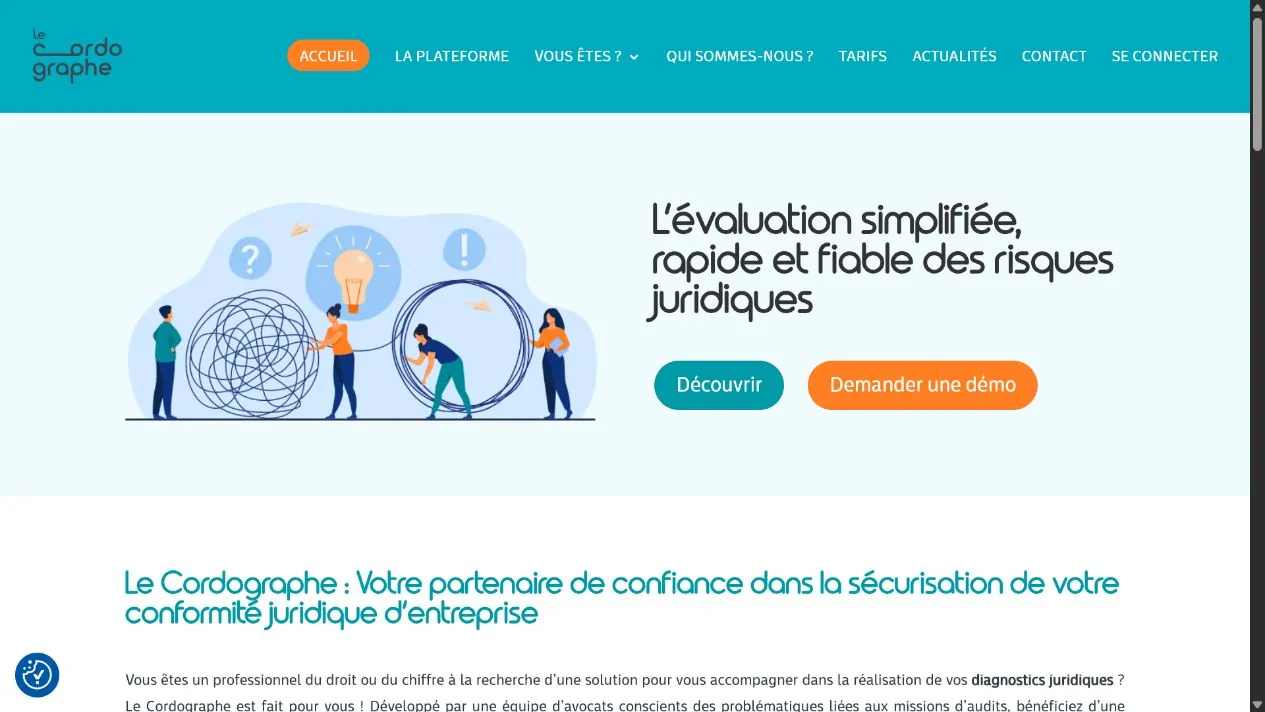
Le Cordographe presents a legal diagnostic platform. Its business website needs to explain the offering, guide legal professionals, executives and prospects, then lead them to demos, pricing, news or contact. When a public site is compromised, the challenge is to stop the visible problem and restore reliability to pages supporting business trust.
Client website
For Le Cordographe, the public website needs to quickly build confidence in the solution, explain relevant audiences and keep essential business actions accessible: discovery, demo requests, pricing, news and contact.
The challenges
The work covered the publicly accessible WordPress website: service pages, demo requests, pricing, news and contact. Cleanup needed to prioritise the business image seen by visitors.
The website needed to be restored without losing useful content, business links and pages helping prospects understand the solution.
The relaunch needed concrete checks: accessible public pages, no suspicious redirects, cleared cache and reviewed access.
What we did
Analysed the WordPress business website to identify what needed to be retained, cleaned or reinstalled.
Rebuilt a clean WordPress foundation, then relaunched the website on its existing hosting.
Cleaned compromised settings and components that could affect public display.
Cleared the cache to prevent damaged versions of the website remaining visible.
Checked administrator access and corrected sensitive areas in WordPress.
Checked public pages, redirects and website responses after cleanup.
Restored a missing logo in the media library to repair the public display.
The same approach, retaining a copy of the infected state before a clean reconstruction, is described step by step on the hacked WordPress website cleanup page.
WordPress foundation
The work restored the public website, retained useful content and verified access to business pages.
The public website presents the offering, visitor profiles, pricing, news, contact and platform access. The work described here concerns that WordPress website.
The work combined website analysis, a clean relaunch, WordPress foundation cleanup and post-intervention checks.
Access, WordPress settings and caches were reviewed to prevent the public website retaining damaged displays after relaunch.
For visitors
The homepage presents legal risk assessment, the platform, relevant audiences, pricing, news and contacts.
Discovery, demo request, login and contact buttons need to remain accessible because they directly connect the website to the business journey.
For a legal solution, the website needs to convey stability and reliability. A redirect or damaged display immediately undermines trust.
Who visits, and why
Understand how the tool supports legal diagnostics and access pages dedicated to their profile.
Identify relevant legal risks, read useful information and move towards a demonstration or contact.
Move quickly from the introduction to a demo request, contact or platform access without visible technical obstacles.
What the project delivers
The items below describe the functions and documented work for this project. They are not measurements of traffic, enquiries or revenue.
The public website was brought back online on a clean foundation, with a usable visitor journey restored.
Pages presenting the offering, demo, pricing, news and contact remain accessible without suspicious redirects or visible disruption.
Risky settings were cleaned and checked after relaunch to reduce the chance of recurrence.
Explore further
Designing a law firm website with several offices.
Read the case study
Designing a law firm website, clear and well-maintained.
Read the case study
Designing a specialist legal website built to last.
Read the case studyOur services